
1-click MMI execution in Android
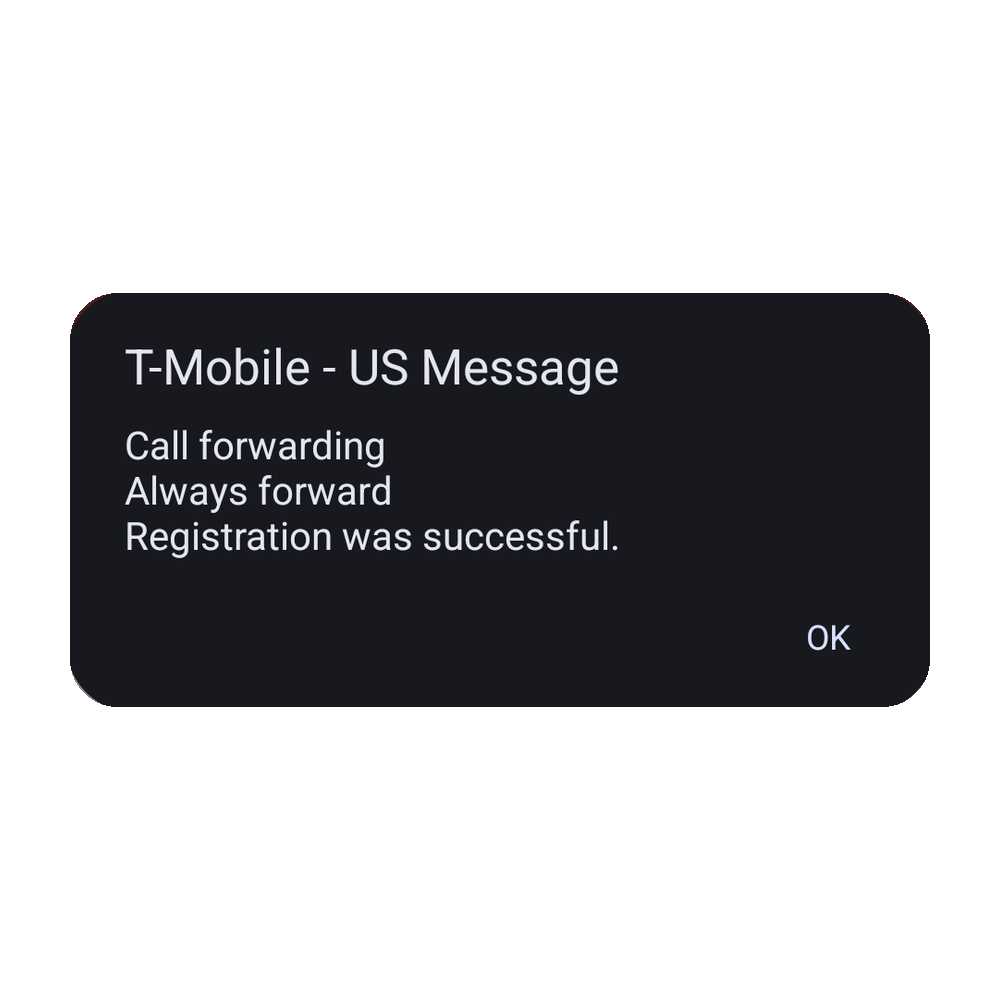
What happened
An application with the CALL_PHONE permission can execute carrier MMI/USSD codes with no user confirmation. A vulnerable application with browsable deeplinks can trigger MMI execution with a single tap.
Summary assembled by rule from the sources below
Why it's spreading
Sources
Community
- 1-click MMI execution in AndroidLobsters